Nizozemski trgovački lanac Albert Heijn (AH), koji je dio grupacije Ahold Delhaize, upravo proživljava veliki kibernetički napad. Zbog ovog “kibernetičkog incidenta” srušene su njihove službene web stranice, mobilne aplikacije te sustavi dostave i korisničke podrške.
Osim ovog najnovijeg napada iz listopada 2026. godine, tvrtka je i ranije bila česta meta hakera
‘Grootste digitale klap ooit’ voor Albert Heijn: klanten lopen over naar Jumbo en Picnic https://t.co/0VcaOpGCeg
— Thuis voor de buis (@TBlerick82657) October 12, 2026
Hakeri podigli temperaturu hladnjaka u francuskim supermarketima na čak 50 stupnjeva
Veliki hakerski napad pogodio je stotine supermarketa diljem Francuske.
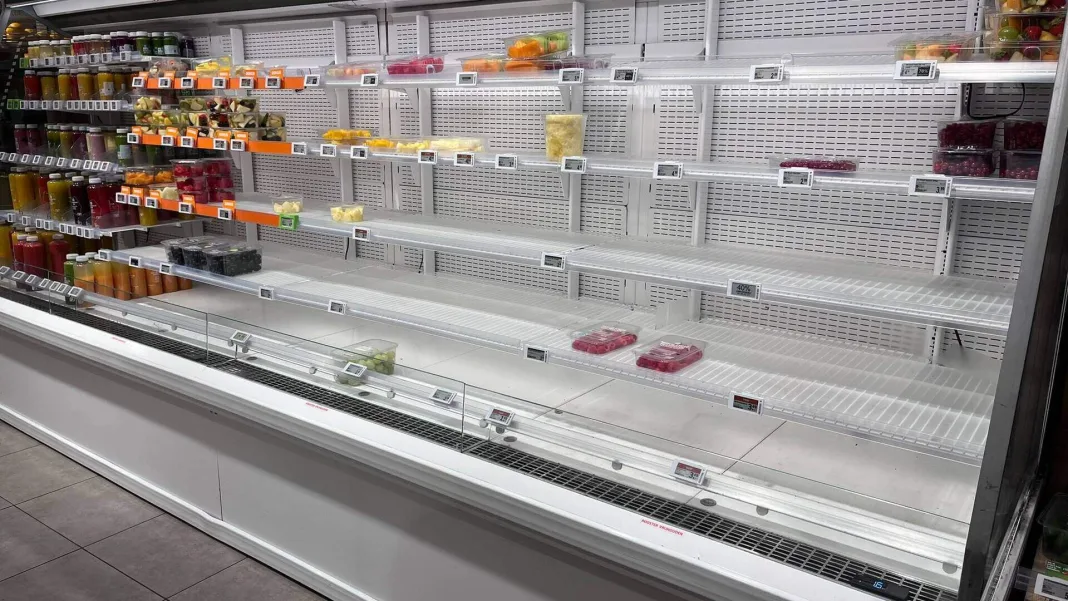
Napadači su preuzeli kontrolu nad rashladnim sustavima i uključili odmrzavanje hladnjaka i zamrzivača, zbog čega su se velike količine hrane pokvarile. Francusko tužiteljstvo pokrenulo je istragu, a prijavljeni su i požari povezani s napadom.
Napad se dogodio tijekom noći s nedjelje na ponedjeljak, a pogodio je neke od najvećih francuskih trgovačkih lanaca, uključujući Intermarché, Netto, Coopérative U, E.Leclerc i Monoprix. Pogođene su i trgovine Carrefoura.
🇫🇷La France est le paradis des hackers! Un pays en ruine qui n’a plus les capacités de se protéger: Intermarché, Monoprix, Carrefour, E. Leclerc… Un piratage d’ampleur a ciblé les infrastructures frigorifiques des grands Supermarchés Français, sabotant un maillon essentiel de la chaîne alimentaire du pays. Les frigos sont montés à 50C° . Une attaque inédite qui touche au ventre de la France… À force de vouloir tout connecter , nous livrons nos vies aux hackers.
— 🇺🇸Trump Times 🇺🇸 (@VirginiePerez15) October 12, 2026
Prema najnovijim podacima koje je objavio AFP, napad je zahvatio najmanje 300 trgovina Intermarchéa i Nettoa, gotovo stotinu trgovina Coopérative U, tridesetak trgovina Monoprixa te nekoliko trgovina E.Leclerca. Carrefour je potvrdio probleme u 80 svojih trgovina.
France’s supermarket refrigeration attack highlights a dangerous OT threat: “sabotage by setpoint”. On 11–12 October, hundreds of stores including Intermarché/Netto, Carrefour, Coopérative U and E Leclerc – reported refrigeration disruption. Temperatures reportedly reached 50°C, with widespread food spoilage and reports of fires. Danfoss systems were implicated; the exact exploit and actor remain unconfirmed. In May, attackers sabotaged an Israeli food plant’s CO₂ refrigeration by changing setpoints, wiping controller configurations and forcing valves open. Three compressors were destroyed, and recovery took about a week. Profero attributes the campaign to IRGC-linked Cyber Isnaad Front, with GRAT malware on the IT network alongside destructive manipulation of OT systems. On 26–27 August, at least six US military commissaries reported refrigeration failures. Fort Huachuca’s freezers entered defrost overnight, spoiling inventory. A DCIS-led investigation followed, but a cyberattack has not been publicly confirmed. Similar damage does not establish a shared actor or campaign. Claroty’s August research documented Danfoss AK-SM 800A vulnerabilities, including CVE-2025-41450, but their use in France remains unconfirmed. Defenders should review exposed controller interfaces and monitor unexpected setpoint, mode and configuration changes. Profero’s “OneDrive Update” task and C2 84.201.6[.]131:7878/9988 are leads specific to the Israeli campaign. Research credits: @ProferoSec and @Claroty
— FalconFeeds.io (@FalconFeedsio) October 12, 2026